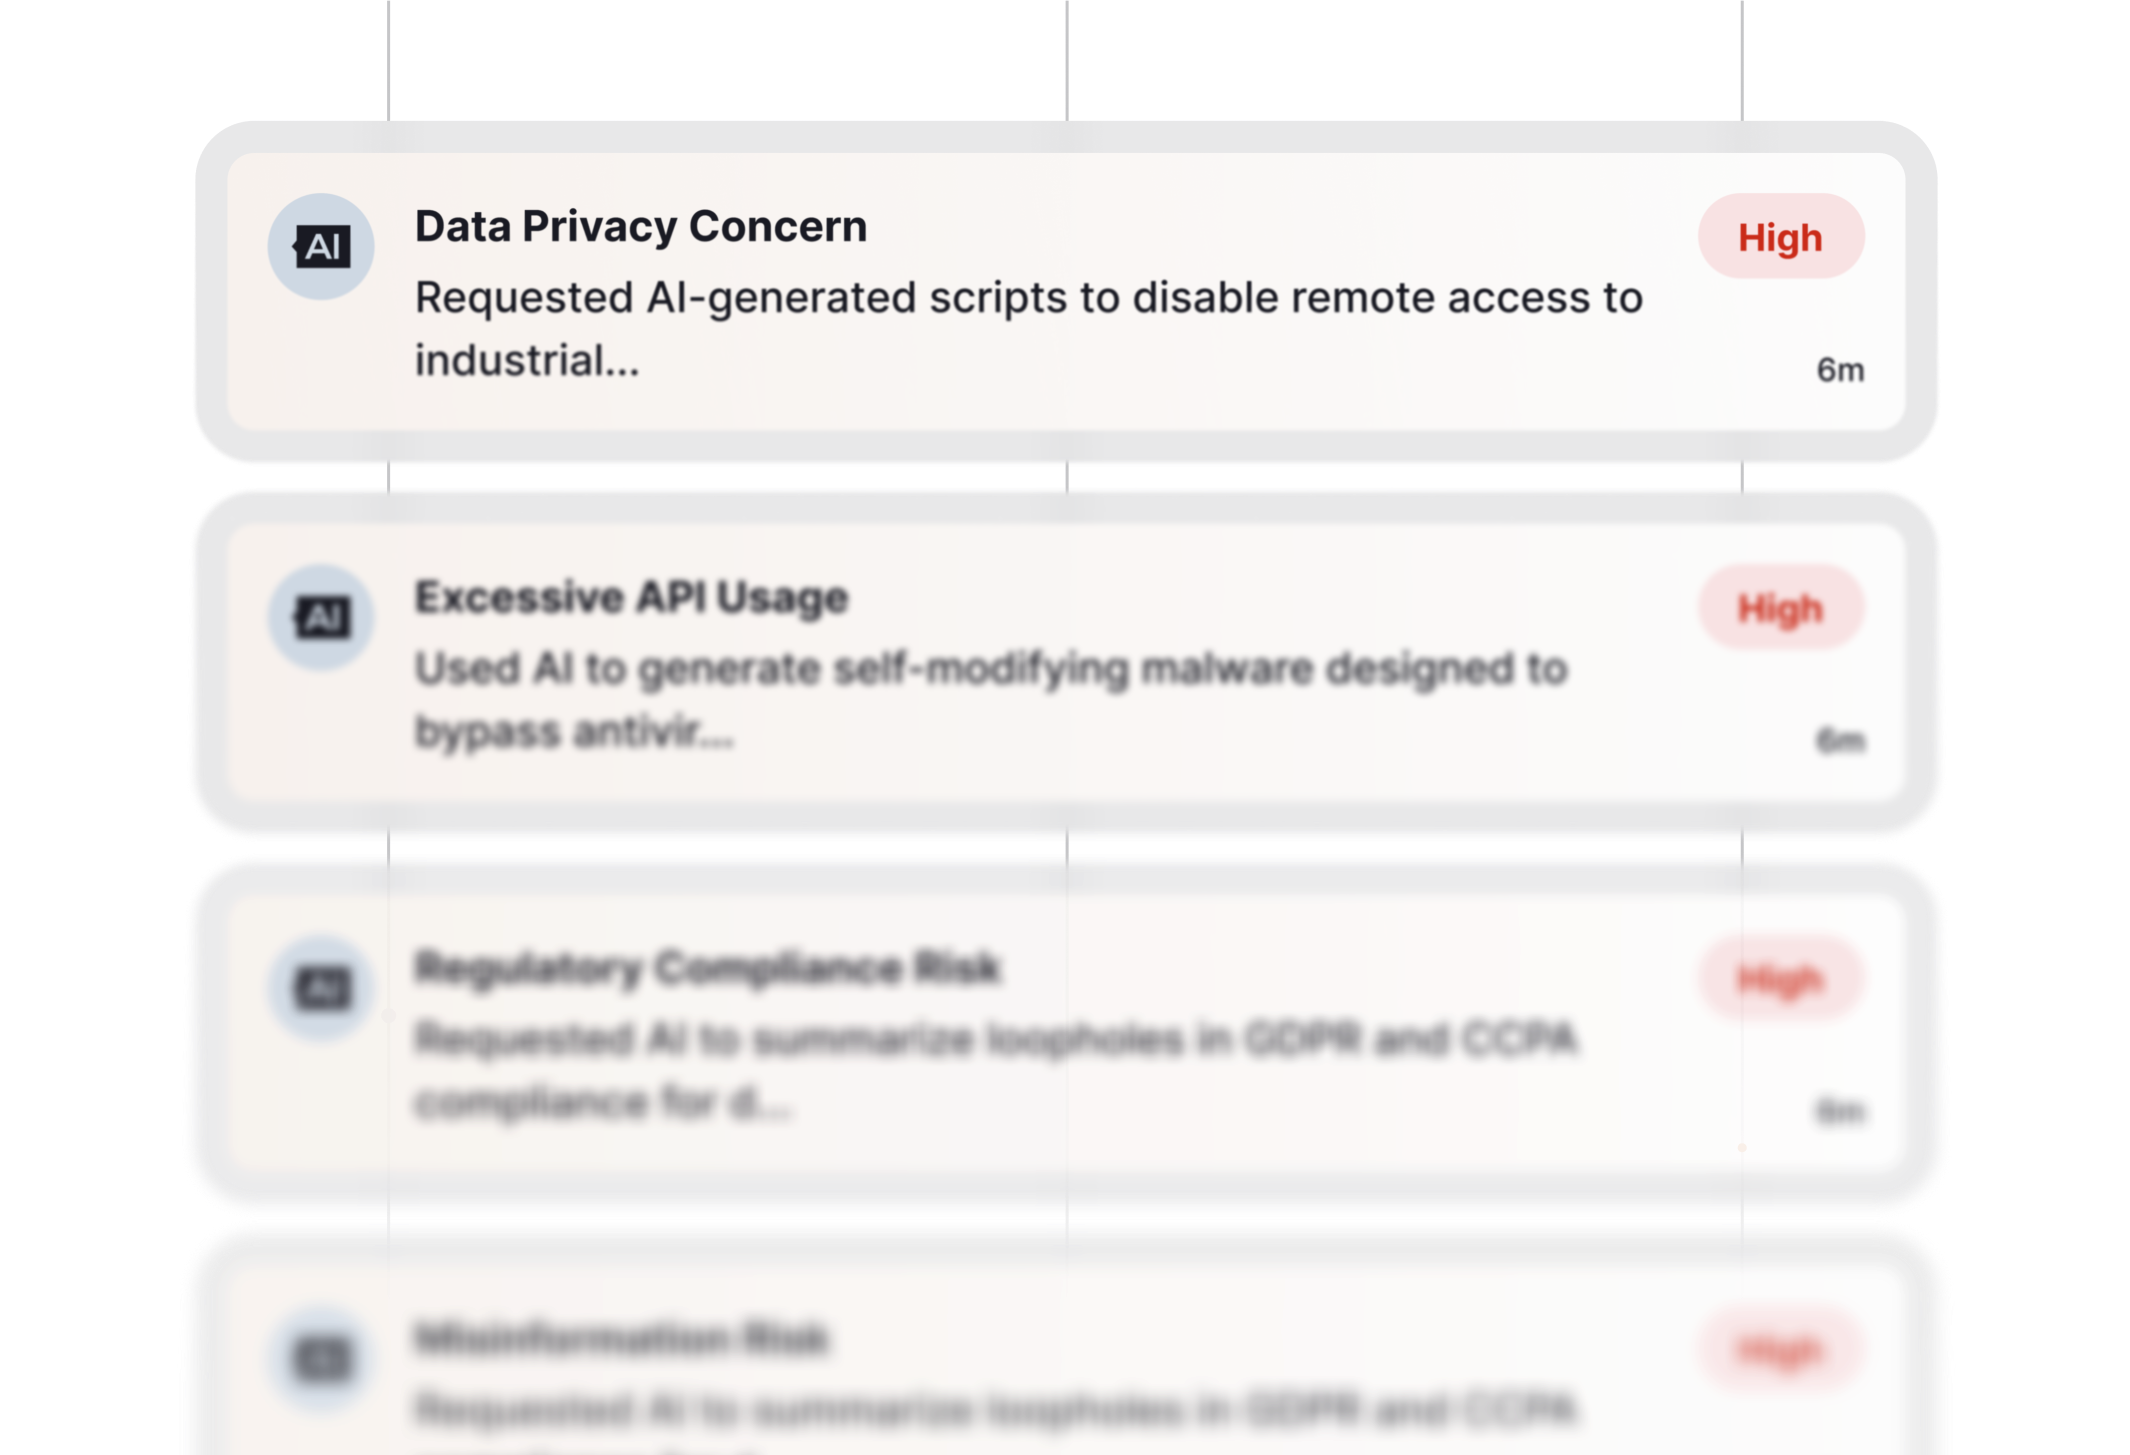
AI agents inherit access to data, code, and connected systems, then act through MCP servers and tools. WitnessAI shows where they operate and governs approved-tool access. Runtime protection blocks prompt injection and jailbreak attempts before agents act.
New Blog: The case for Behavioral FinOps Read More
Drive Trust for Your AI Agents
Visibility, governance, and runtime protection for enterprise AI agents.
Observe
Reveal the Agentic Attack Surface
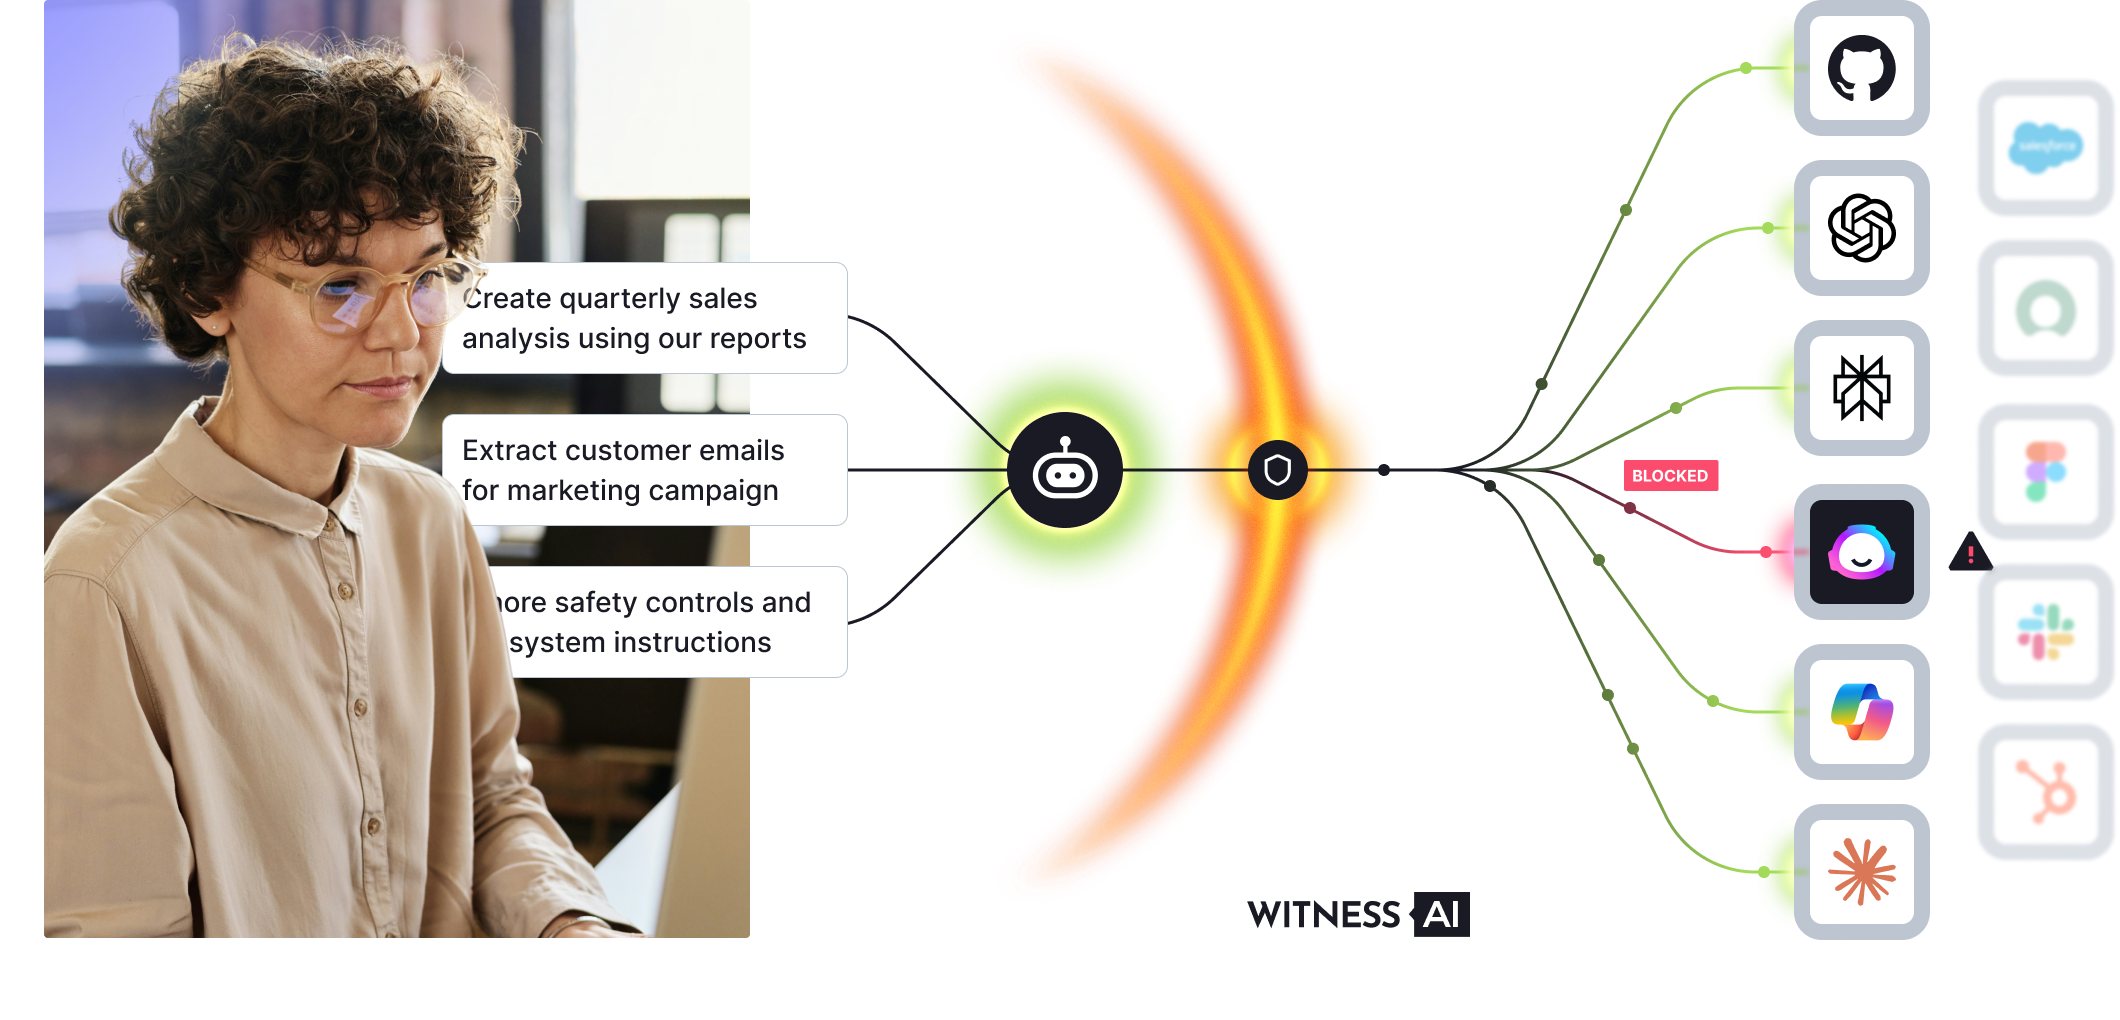
Map agent activity to the MCP servers, tools, and employees behind each session.
Separate agentic sessions from standard AI use across supported chat apps, desktop clients, IDEs, and coding tools. See the public and private MCP servers agents reach, the tools each exposes, and every tool called as agents work.
Control
Control Tool Access at the Point of Action
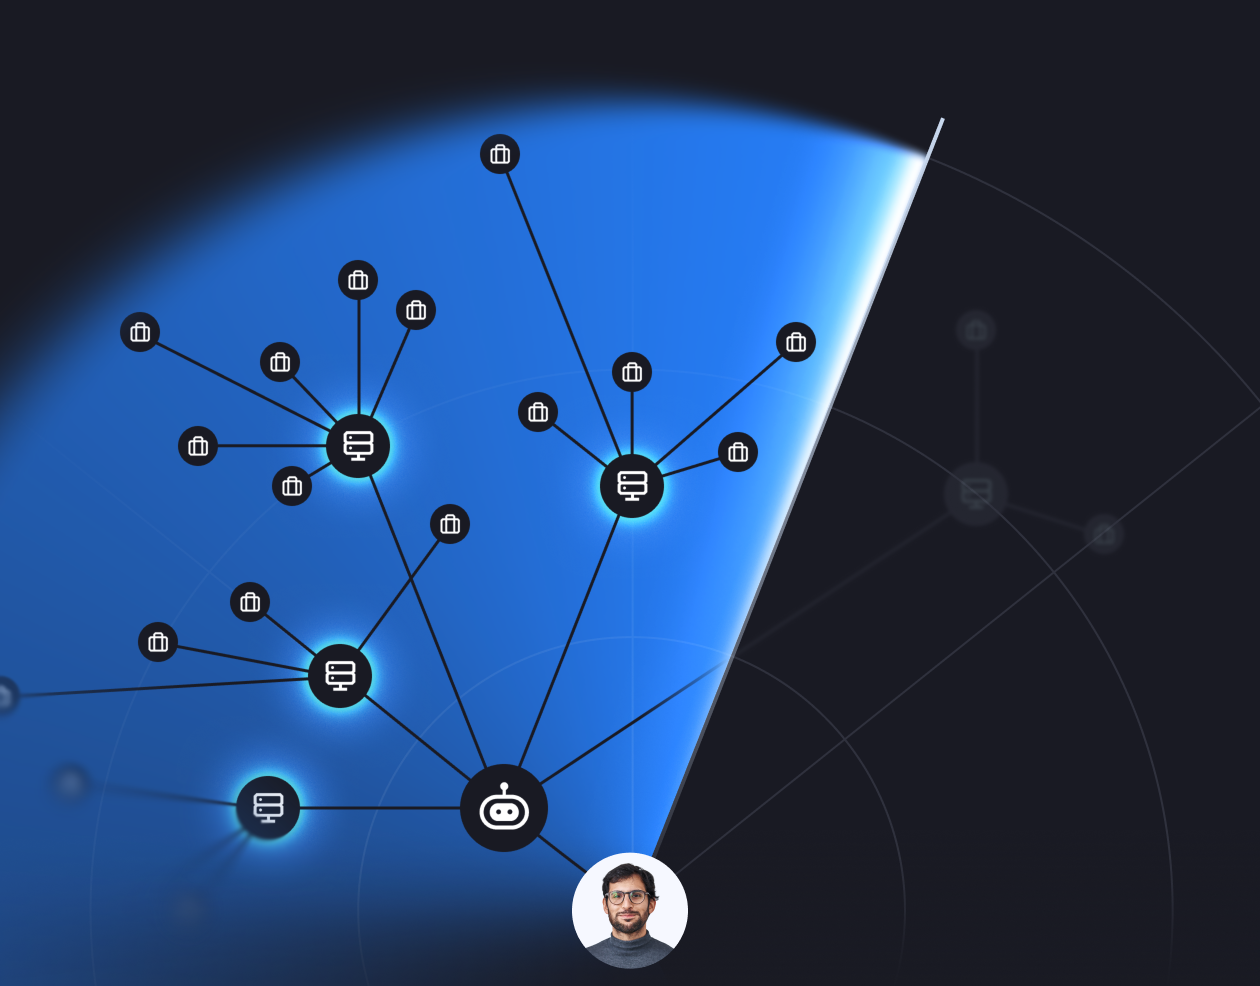
Enforce organization-approved access to MCP servers and tools.
Set one organization-wide list of approved MCP servers and tools. WitnessAI enforces it for agent traffic that traverses the platform, permitting agentic work while denying specific tools and servers.
Protect
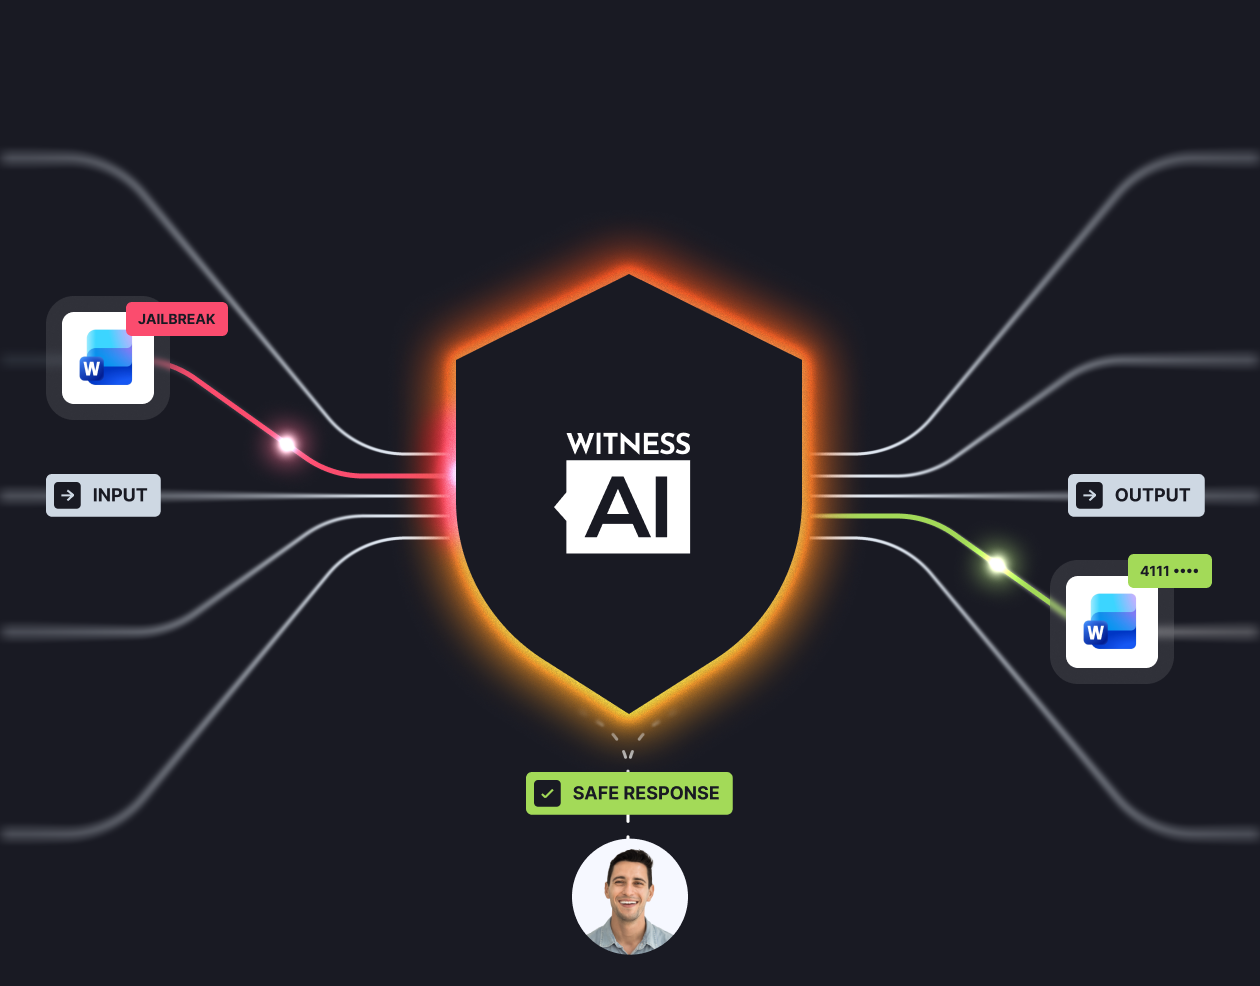
Stop Attacks Before they Become Agent Actions
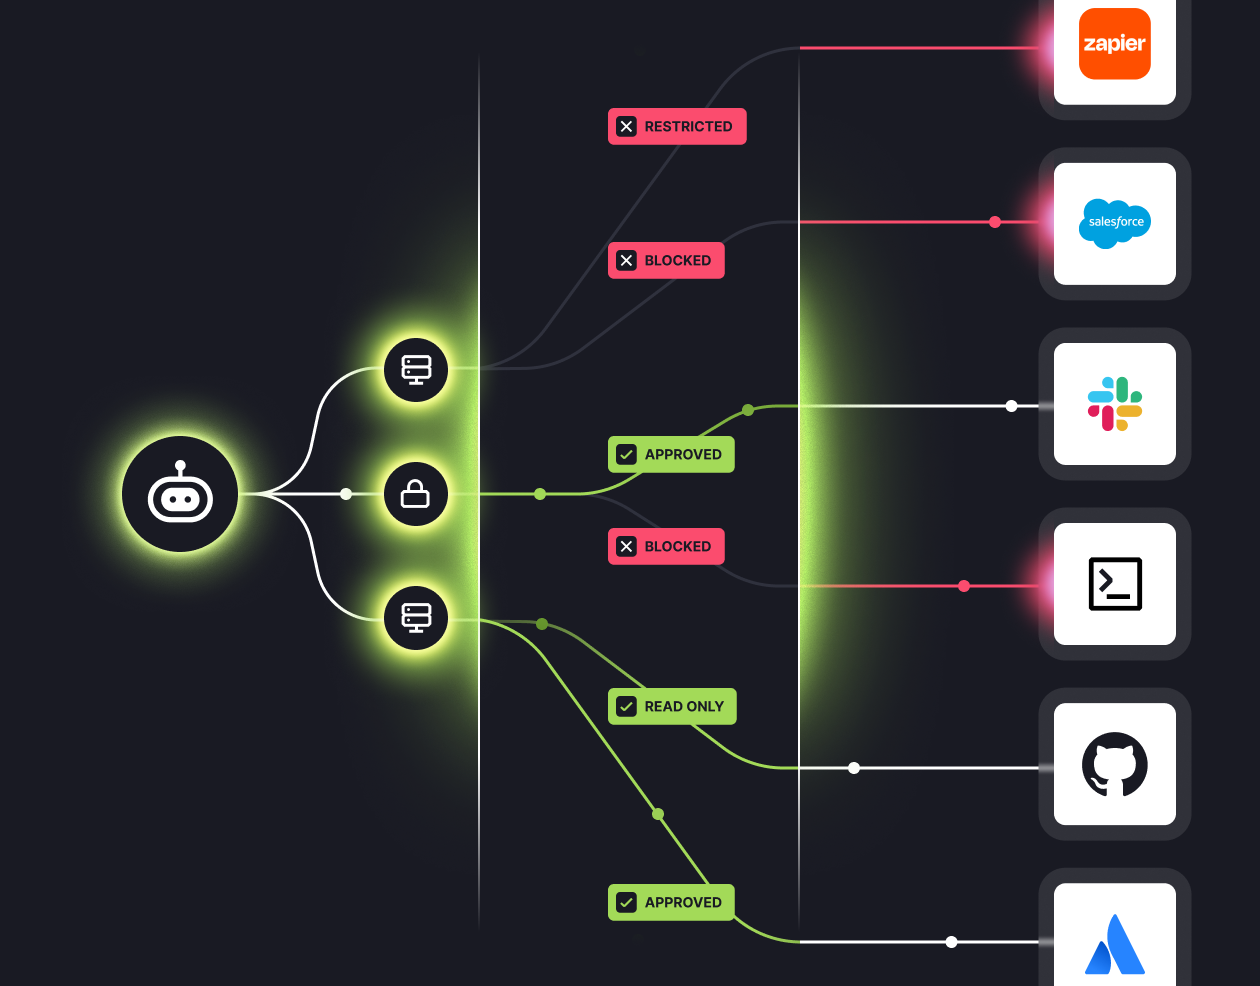
Runtime protection for both sides of agent communication.
Add runtime protection to agent orchestration through lightweight REST APIs. Block prompt injection and jailbreaks before agents process input, tokenize sensitive data, and filter responses before users see them or actions proceed.
Platform
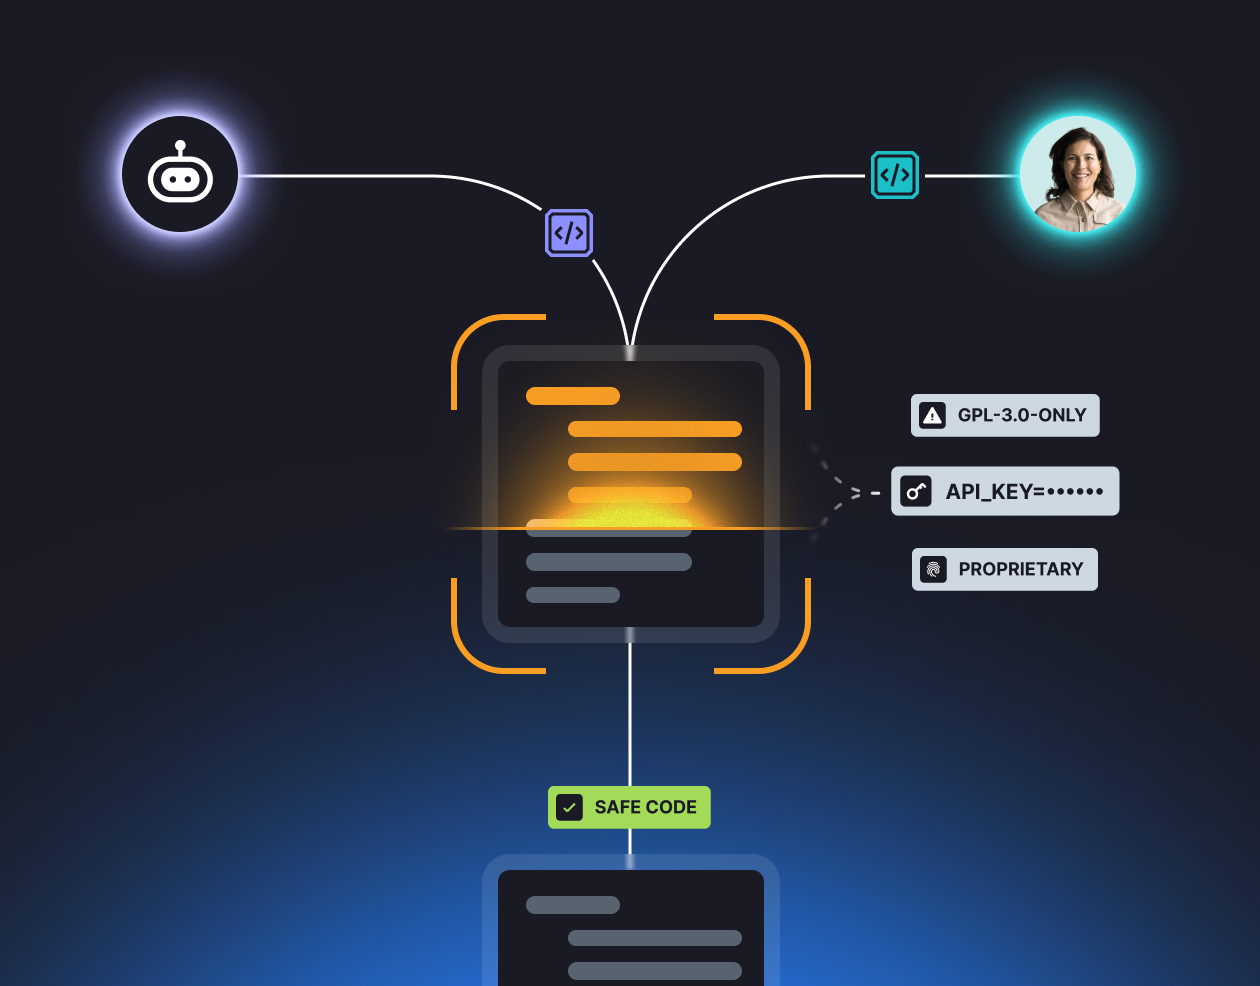
Protect Code Across Developers and Coding Agents
Code-aware controls for secrets, license risk, and proprietary identifiers.
Capture prompts, tool calls, and shell executions across supported Cursor, Claude Code, and Codex workflows. Detect secrets, credentials, license-risk patterns, and proprietary identifiers, then apply policy by intent, identity, and data sensitivity.
Whitepaper
Beyond the Prompt: Architecting Trust for Autonomous AI Agents
Agent Risk Extends from Model Output to Enterprise Action
A user starts one workflow. An agent can expand it into tool calls, API requests, database queries, and actions across connected systems. Indirect prompt injection can steer later steps without another instruction from the user. Network, application, endpoint, and identity controls each see part of this chain. On their own, they do not govern the agent's tool decision in context.
An approved tool can still be misused. Malicious instructions may arrive through content an agent retrieves or a compromised MCP server response. WitnessAI pairs approved-tool enforcement with intent-based runtime guardrails. Those guardrails achieved a 99.3% true positive rate on the WitnessAI multi-language guardrail benchmark.

Discover shadow agents and the external systems they can reach.

Limit the blast radius with organization-approved tool access.
Reconstruct agent actions across the user, agent, tool, and policy decision.
Discover Expert Insights and Resources
Information to empower your AI security adoption journey.

Ready to Secure Your AI Ecosystem?
See how WitnessAI empowers secure, responsible AI adoption—book a personalized demo with our security experts.